Java4Shell - Remote Code Execution (CVE-2026-114938)
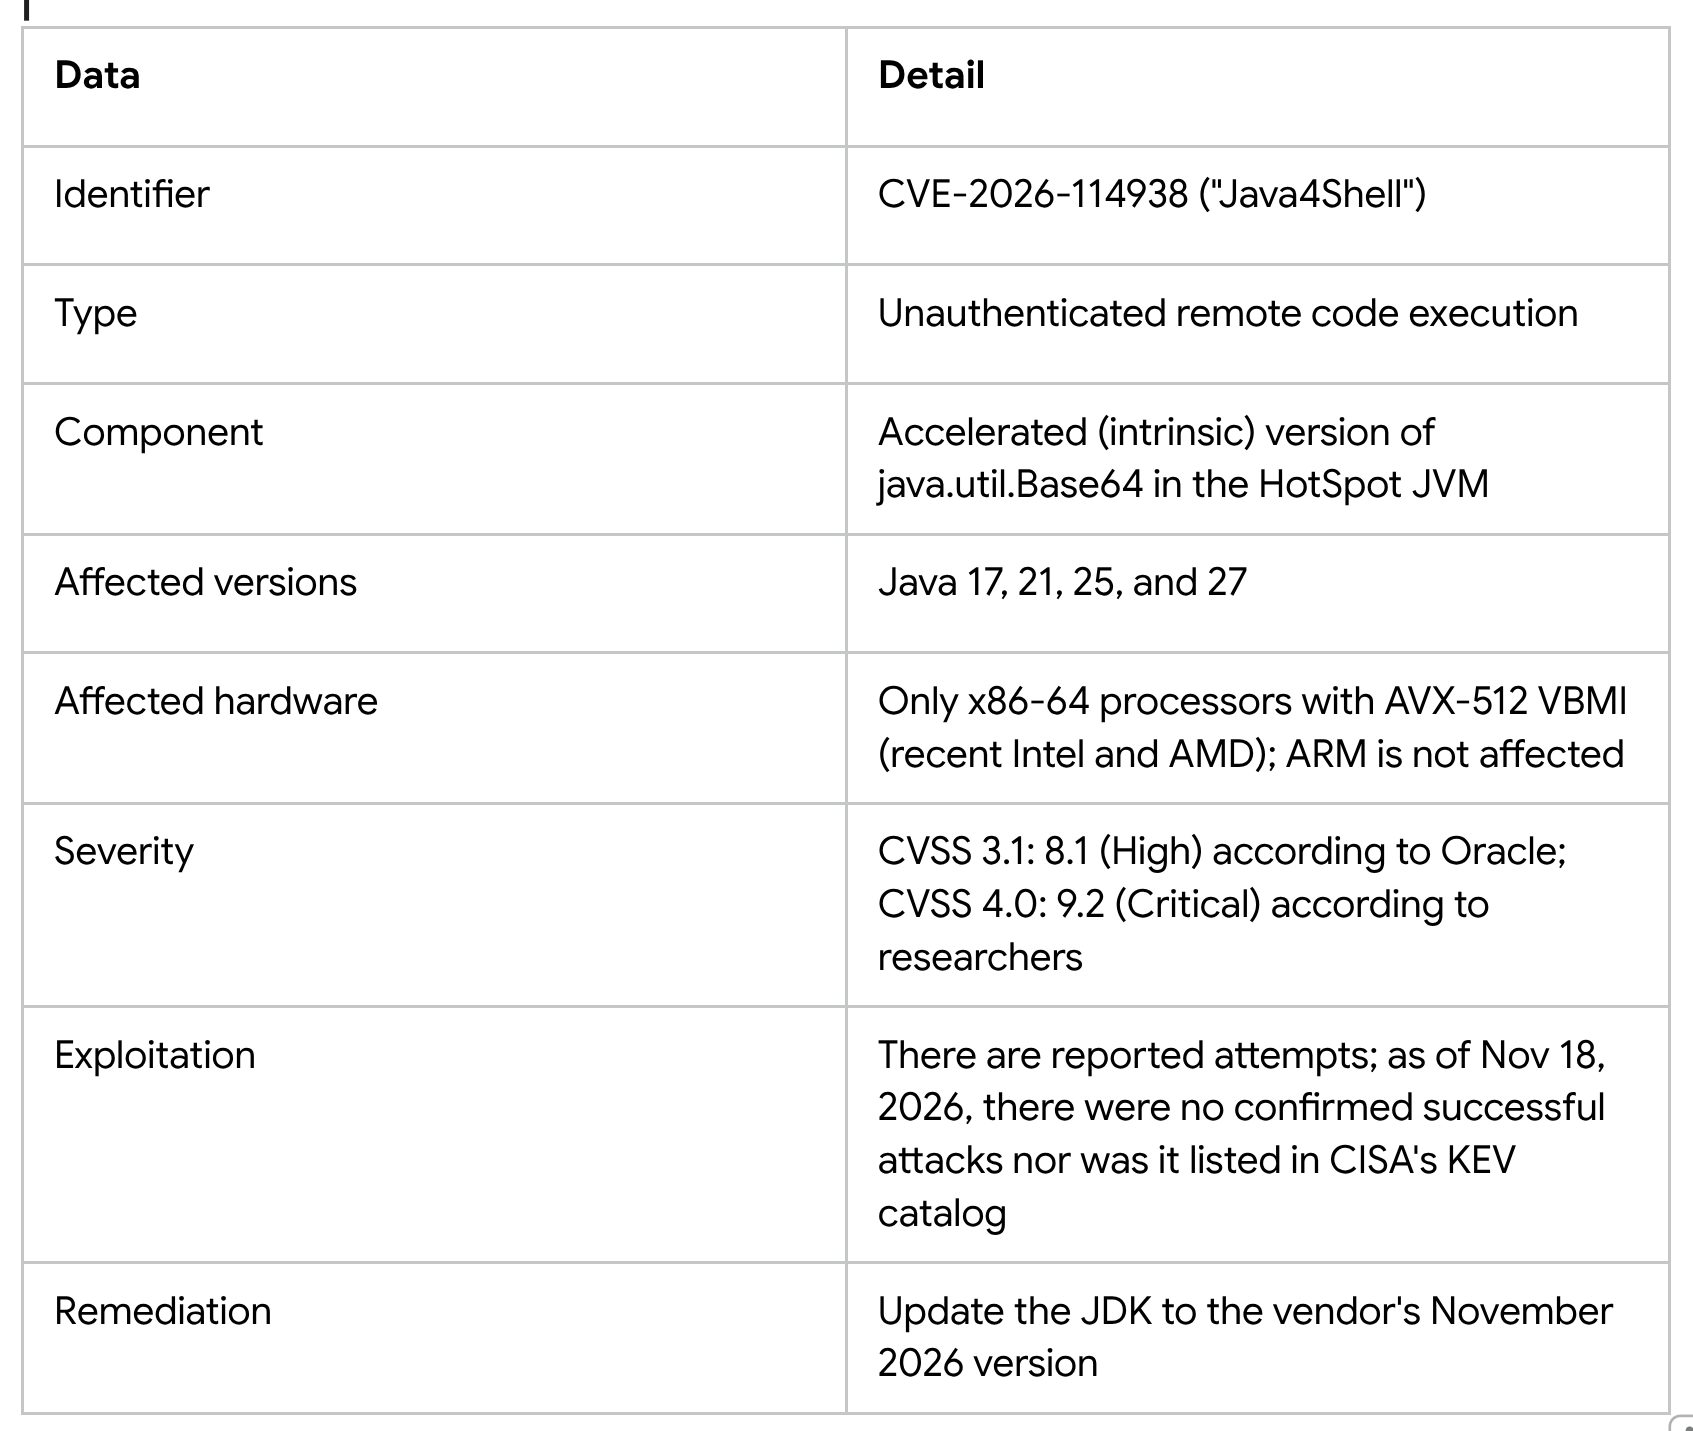
On November 17, 2026, Java4Shell (CVE-2026-114938) was disclosed, a Java vulnerability that allows unauthenticated remote code execution. This means an attacker could execute unauthorized instructions on an affected server simply by sending crafted data to the application.
ToogleBox runs on Google App Engine, Google Cloud's managed platform. Under this model, Google is responsible for managing the infrastructure, servers, and Java runtime environment, including applying security patches. Its specialized teams are already working on the corresponding mitigations, and the permanent solution will arrive once Google updates the Java environment and confirms it in its official bulletins.
As a preventive measure, and while Google deploys the permanent patch, ToogleBox's engineering team has implemented a mitigation measure that completely blocks the exploitation path of this flaw. We have configured our application with the -XX:-UseBASE64Intrinsics parameter, which disables the specific Java component affected by the vulnerability and forces the use of a secure alternative implementation.
The vulnerability
Java4Shell is a memory corruption flaw in OpenJDK's optimized Base64 decoder. Oracle and OpenJDK disclosed and patched it on November 17, 2026.